A cookie policy is a page that lists the cookies your site uses, what each one does, how long it lasts, and how visitors can say no.
If you have visitors in the EU or UK and use analytics, ads, or embeds, you need one. Below: what to put in it, 3 ways to write it, how to publish it on WordPress, and where to link it.
What you need depends on 2 things: what your site does (analytics, ads, embeds, a store) and where your visitors are. A blog with no tracking and only local visitors needs much less than a store that runs ads to EU and Indian customers.
What is a cookie policy?
Cookies are small text files a site stores in the visitor’s browser. Some keep the site working. Others track visitors for analytics and ads.
A cookie policy explains those cookies in plain language. It answers 4 questions for the visitor:
- Which cookies does this site use?
- Why?
- Who else gets the data?
- How do I refuse or change my choice?
The cookie policy and the cookie banner do different jobs. The policy explains. The cookie banner asks for consent and blocks cookies until the visitor agrees. You need both. More on the difference: cookie notice vs cookie policy.
Disclosure vs consent: 2 separate duties
Privacy laws ask for 2 different things. A cookie policy handles the first. A cookie banner handles the second.
| Disclosure (tell people) | Consent (ask people) | |
|---|---|---|
| What it means | Give clear information about each cookie: what it does, who sets it, how long it lasts | Get a clear “yes” before a non-essential cookie is set |
| Where it comes from | ePrivacy Directive Art. 5(3) (“clear and comprehensive information”). GDPR Art. 5(1)(a) (processing must be lawful, fair, and transparent) and Art. 12 to 13 (what you must tell people, in clear language) | ePrivacy Directive Art. 5(3) and UK PECR reg. 6 (consent before storing or reading non-essential cookies). GDPR Art. 4(11) and Art. 7 (what valid consent is, proof of consent, withdrawal as easy as giving) |
| Applies to | Every cookie you set, as good practice. Required for any cookie that processes personal data | Non-essential cookies only |
| Tool that does it | Cookie policy (and privacy policy) | Cookie banner (consent management platform) |
A cookie policy on its own doesn’t get consent. A banner on its own doesn’t give enough information. Each one links to the other.
Do you need a cookie policy?
It depends on where your visitors are and what your site does.
EU and UK visitors
The ePrivacy Directive (Art. 5(3)) and the UK’s PECR (reg. 6) say you must give “clear and comprehensive information” about cookies and get consent before you set non-essential ones. A cookie policy is the standard way to give that information.
GDPR applies on top when cookies collect personal data, which most analytics and ad cookies do. GDPR Art. 13 lists what you must tell people when you collect their data, including the purpose, the recipients, how long you keep it, and their rights. See ePrivacy Directive vs GDPR.
California visitors
The CCPA does not require a separate cookie policy. It requires a privacy policy that discloses the data you collect, including through cookies, and a “Do Not Sell or Share My Personal Information” link if you sell or share data. Sharing data with ad platforms for cross-context behavioral advertising (for example, retargeting pixels) counts as “sharing”. You must also honor Global Privacy Control (GPC) signals as an opt-out.
The CCPA applies to for-profit businesses that meet 1 of these:
- Over $26,625,000 in annual revenue (2025 amount, adjusted every 2 years)
- Buy, sell, or share data on 100,000+ California consumers or households
- Earn 50%+ of revenue from selling or sharing data
Who enforces it. The California Privacy Protection Agency and the Attorney General enforce most of the CCPA. Private lawsuits under the CCPA are limited to one case: a data breach caused by a failure to keep reasonable security (Cal. Civ. Code § 1798.150). Statutory damages are $107 to $799 per consumer per incident (2025 amounts). There is no private right to sue under the CCPA for a missing cookie policy or banner.
Separately, some plaintiffs have sued sites over tracking pixels and chat tools under the California Invasion of Privacy Act (CIPA), a wiretapping law. Courts have decided these cases differently. If you run ad pixels or session-replay tools for California visitors, ask a lawyer about your exposure.
See our CCPA guide.
Visitors in India
India’s Digital Personal Data Protection Act 2023 (DPDP Act) and the DPDP Rules 2025 apply to digital personal data processed in India, and to processing outside India when you offer goods or services to people in India.
The DPDP Act doesn’t mention cookies by name. It applies to cookies and trackers that collect personal data, such as a device ID linked to a person. What it asks for:
- A notice before or with the consent request (Section 5, Rule 3). It must stand on its own, be in clear and plain language, list the personal data and the specific purpose, and explain how to withdraw consent, use rights, and complain to the Data Protection Board.
- Consent that is free, specific, informed, unconditional, and unambiguous, given by a clear affirmative action (Section 6). Withdrawal must be as easy as giving consent.
- Language options. People can ask for the notice in English or any of the 22 languages in the Eighth Schedule of the Constitution.
- Children. For users under 18, you need verifiable consent from a parent. You must not track or monitor children’s behavior, or target ads at them (Section 9).
- Consent managers. People can give and manage consent through a consent manager registered with the Data Protection Board.
Dates. The DPDP Rules were notified on 14 November 2025. The consent manager rules apply from 14 November 2026. The notice and consent duties apply from 14 May 2027. Penalties go up to ₹250 crore per breach.
For a site with Indian visitors, a cookie policy that lists each tracker, its purpose, and how to withdraw consent covers most of the notice requirement. Link it from the consent request.
Everyone else
Many privacy laws ask you to disclose tracking, and Google AdSense asks publishers to disclose cookie use. A cookie policy is the simplest way to do it.
What your site does decides what you need
| Your site | What you need |
|---|---|
| Only strictly necessary cookies (login, cart, security) | No consent. List the cookies in your cookie policy or privacy policy as good practice |
| Analytics (Google Analytics, Matomo with cookies, Hotjar) | Cookie policy. Consent banner for EU visitors. UK: possible exemption (see below) |
| Ads, retargeting pixels, social media embeds | Cookie policy, consent banner for EU, UK, and India. “Do Not Sell or Share” link and GPC for California |
| A store or membership site with accounts | Cookie policy and a full privacy policy covering orders, accounts, and payments |
| A site aimed at children | Extra rules: COPPA in the US, parental consent under the DPDP Act in India, and stricter defaults under GDPR. Get legal advice |
If your site sets only strictly necessary cookies (login, cart, security), you don’t need consent for them. You should still list them in your cookie policy or privacy policy.
Essential vs non-essential cookies
This split decides which cookies need consent.
| Essential (strictly necessary) | Non-essential | |
|---|---|---|
| What they do | Keep the site working: login, cart, security, saving the visitor’s cookie choice | Analytics, ads, social media, embeds, some preference cookies |
| Examples | WordPress login cookie, WooCommerce cart cookie | Google Analytics _ga, Meta Pixel _fbp, YouTube embed cookies |
| Consent needed under ePrivacy and GDPR? | No | Yes, before the cookie is set |
| List in the cookie policy? | Yes | Yes |
A cookie counts as strictly necessary only if the site, or a feature the visitor asked for, can’t work without it. “It helps our marketing” does not qualify.
UK change. Since 5 February 2026, the UK’s Data (Use and Access) Act 2025 lets 2 kinds of low-risk cookies run without consent: cookies used only to collect statistics to improve the site, and cookies used only for the site’s appearance or functions. Both need clear information about the purpose and a free, simple way to object. Ad and cross-site tracking cookies still need consent. Asking consent for all non-essential cookies still works in the UK. Get advice before you rely on the exceptions, and list exempt cookies in your policy either way.
More on each type: types of internet cookies, session cookies, analytical cookies, and Google Ads cookies.
What to include in a cookie policy
Use this checklist. It is based on ePrivacy Art. 5(3) and GDPR Art. 12 to 13. A policy that ticks every box still needs to match what your site actually sets.
About the policy
- Your business name and website URL.
- The date the policy was last updated.
- A short, plain explanation of what cookies are, including similar tools such as pixels and local storage.
The cookies
- The categories you use: strictly necessary, preferences, analytics, marketing.
- For each cookie: name, provider (you or a third party), purpose, and duration.
- Whether each cookie is first-party or third-party.
- What data the cookies collect, such as a device ID or IP address.
Sharing and storage
- Third parties that receive data through cookies, for example Google or Meta, with a link to their privacy policies.
- Whether data leaves the EU or UK, and how it is protected.
Consent and control
- Which cookies need consent and which don’t, and why.
- How the visitor accepts, refuses, or changes their choice, with a link or button that opens your cookie settings.
- That visitors can withdraw consent at any time, as easily as they gave it.
- How to block or delete cookies in the browser.
Rights and contact
- The visitor’s rights under GDPR (access, deletion, objection) and how to use them.
- A link to your privacy policy for the full detail on personal data.
- How to contact you with questions.
What each cookie field means
Your cookie table needs 1 row per cookie. Here is what goes in each column, and where to find it.
| Field | What to write | Where to find it |
|---|---|---|
| Cookie name | The exact name the browser shows, for example _ga | Cookie scan, or your browser’s developer tools (Application > Cookies) |
| Provider | Who sets it: “This website” or the company, for example Google | Cookie scan. The cookie’s domain tells you who set it |
| First-party or third-party | First-party if set on your domain. Third-party if set on another domain, such as facebook.com | The Domain column in developer tools |
| Category | Strictly necessary, preferences, analytics, or marketing | Your own judgment, using the strictly necessary test above |
| Purpose | 1 plain sentence on what it does for you and the visitor | The provider’s documentation |
| Data collected | For example: a random ID, pages viewed, IP address, device type | The provider’s documentation |
| Duration | Session (deleted when the browser closes) or a time, for example 2 years | The Expires column in developer tools, or the provider’s documentation |
| Privacy policy link | A link to the provider’s privacy policy | The provider’s website |
Before you write anything, run a cookie scan. You can’t list cookies you don’t know about. A cookie scanner, such as the one in WPLP Cookie Consent, finds and sorts them. Run it again each time you add a plugin, form, embed, or tracking tool, then update the policy.
Cookie policy example
Here is a complete cookie policy for a small WordPress store, Northfield Candles (a made-up business). The site runs WooCommerce, Google Analytics 4, the Meta Pixel, and YouTube embeds. The notes in italics explain each section. Remove them from your own policy. Your cookie names, providers, and durations come from your own scan.
Cookies we use
| Cookie | Provider | Category | Purpose | Duration |
|---|---|---|---|---|
wordpress_logged_in_* | This website | Strictly necessary | Keeps you logged in to your account | Session |
woocommerce_cart_hash | This website | Strictly necessary | Remembers the items in your cart | Session |
_ga | Analytics | Tells visits apart so we can count visitors and see which pages they use | 2 years | |
_fbp | Meta | Marketing | Lets us show you our ads on Facebook and Instagram, and measure them | 90 days |
When we ask for your consent
We set strictly necessary cookies without asking, because the website can’t work without them. We set analytics and marketing cookies only after you agree in our cookie banner. Until then, they stay blocked.
How to change your choice
You can change or withdraw your consent at any time. Click “Cookie settings” at the bottom of any page and switch each category on or off. You can also block or delete cookies in your browser settings. If you block strictly necessary cookies, parts of the website, such as the cart, may stop working.
Short sentences, one cookie per row, and a clear way to say no. That is the standard to aim for in every section on the checklist.
How to create a cookie policy in WordPress with WPLP Legal Pages
WPLP Legal Pages generates legal pages from a questionnaire and publishes them in WordPress.
The cookie policy templates are on paid plans. There are 2: GDPR Cookie Policy for EU and UK visitors, and Cookies Policy for sites outside the EU and UK. The Free plan includes 4 other templates: Standard Privacy Policy, Terms of Use, DMCA, and Standard CCPA.
Step 1: Install the plugin
- In WordPress, go to Plugins > Add New.
- Search for WPLP Legal Pages.
- Click Install Now, then Activate.
Step 2: Add your business details
Open WP Legal Pages in the admin menu. Fill in your business profile: domain, business name, contact details, and address.
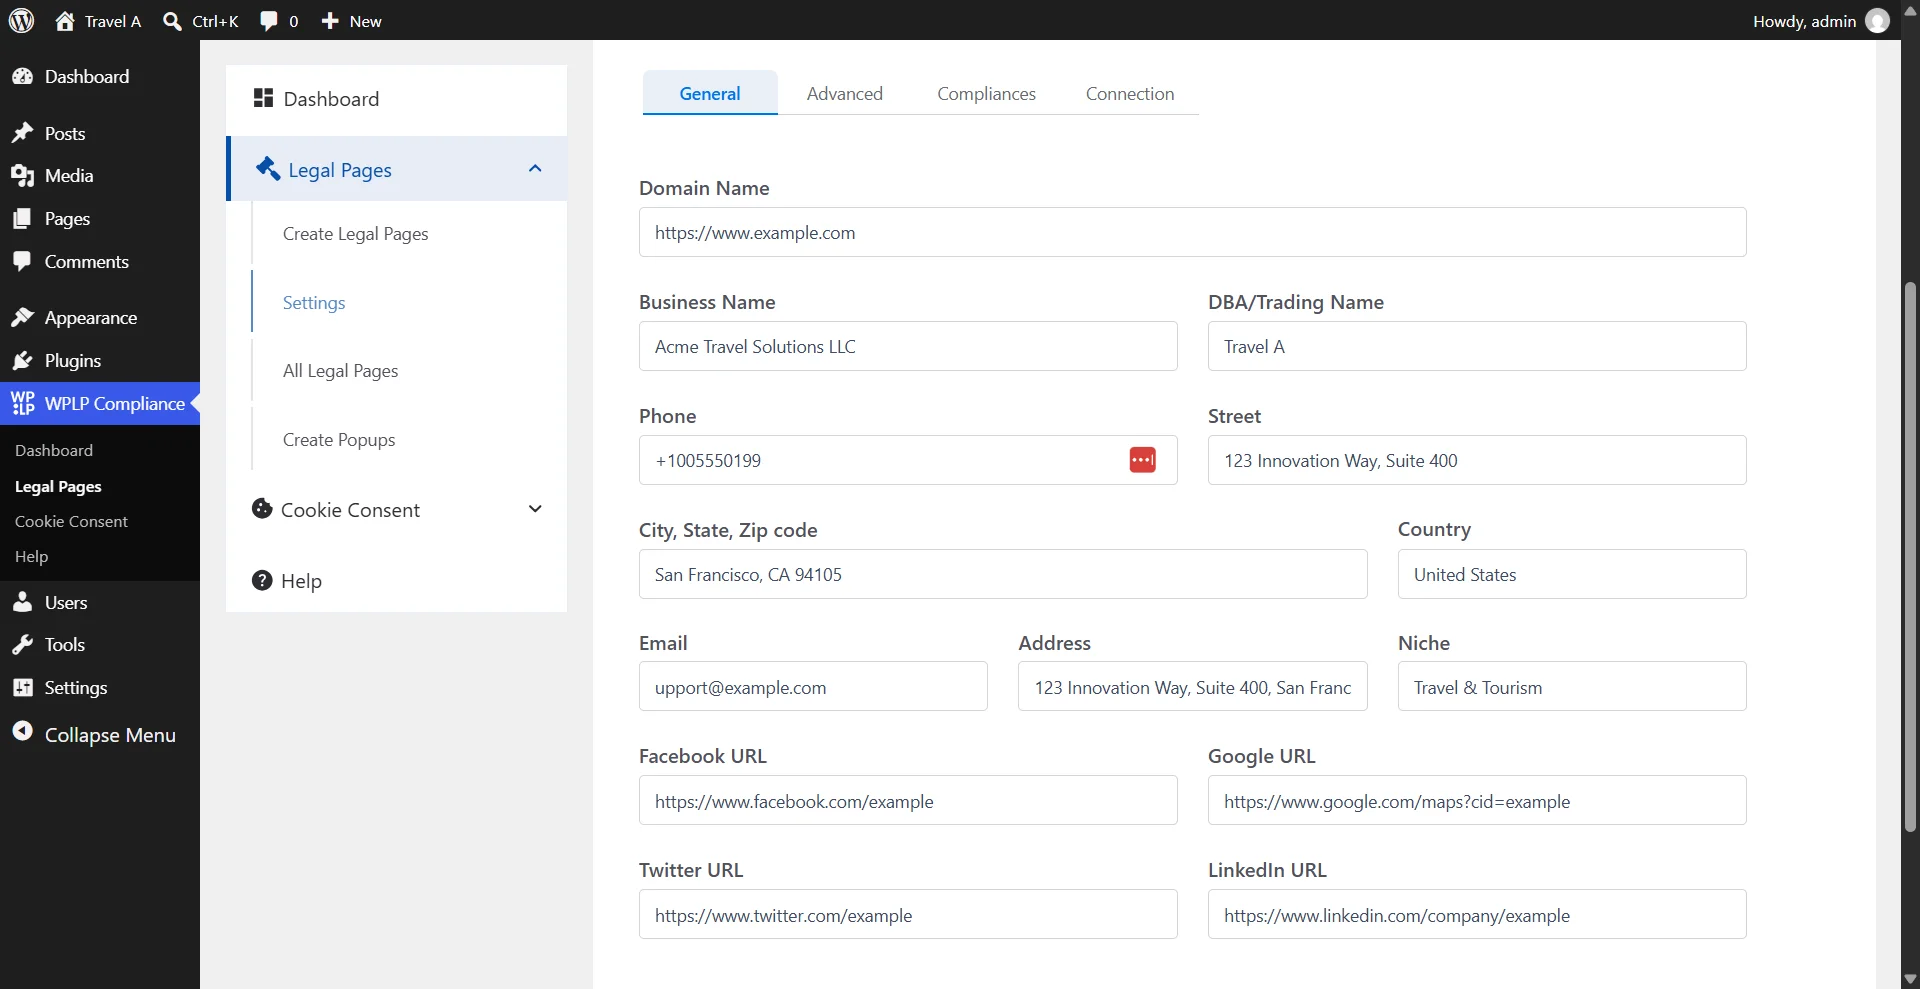
You enter these once. Every legal page you generate uses them.
Step 3: Choose a paid plan
Buy a plan on the pricing page:
| Plan | Price | Sites |
|---|---|---|
| Professional | $8/month or $48/year | Up to 3 |
| Business | $12/month or $72/year | Up to 10 |
| Agency | $28 to $98/month | 25, 50, or 100 |
The pro templates turn on in the plugin you already have. Nothing to reinstall. Every plan includes the full template library of 30+ templates, so the same plan also covers a GDPR privacy policy, terms and conditions, and disclaimers.
Step 4: Pick the cookie policy template
Go to Create Legal Pages and choose:
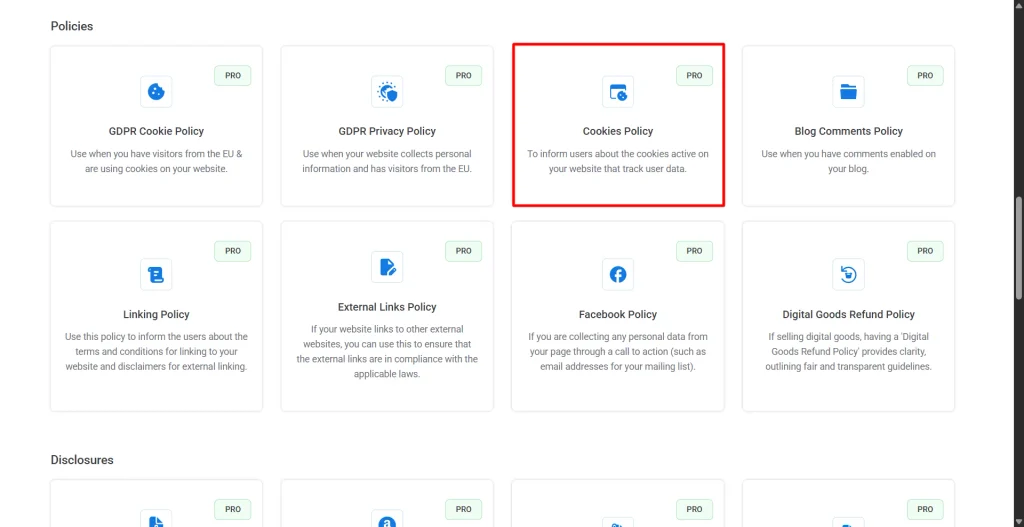
- GDPR Cookie Policy if you have visitors in the EU or UK.
- Cookies Policy if you don’t.
More on the template: GDPR cookie policy generator.
Step 5: Answer the questionnaire
The wizard asks about your site and the cookies you use. Have your cookie scan results open, so your answers match what the site actually sets.
Step 6: Review, edit, and publish
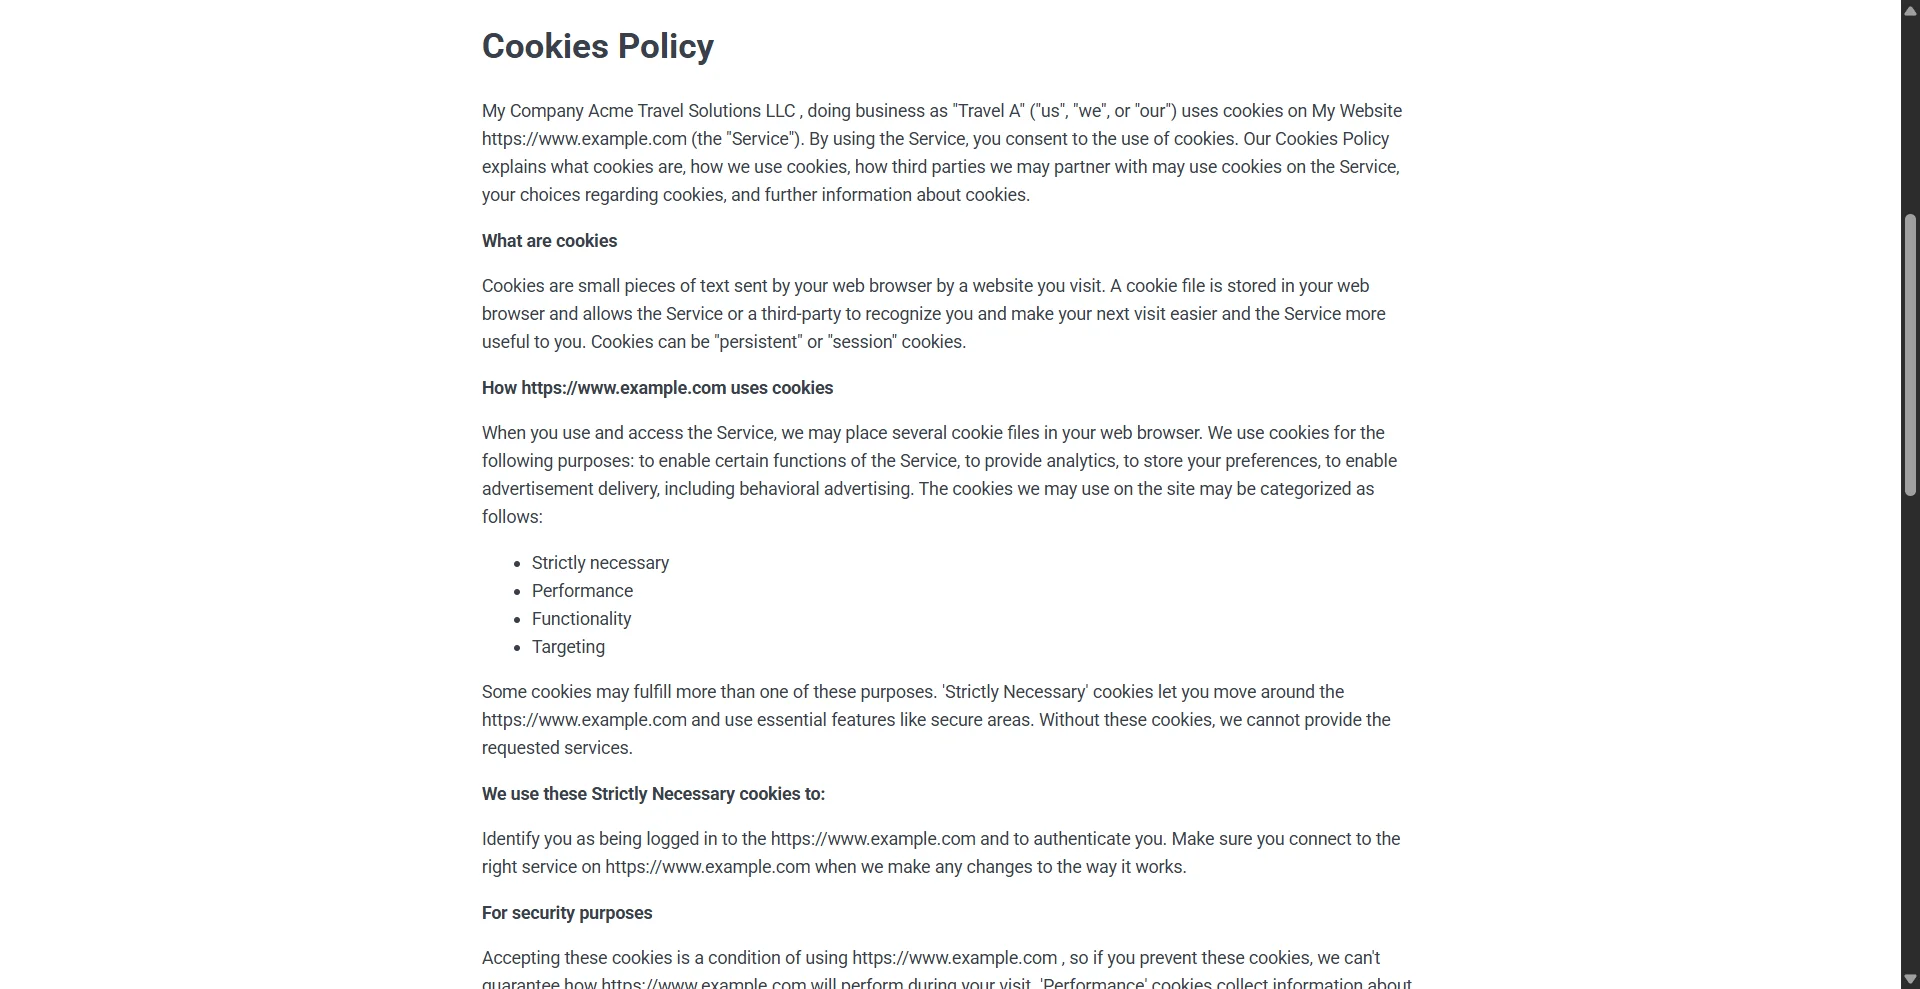
Preview the generated policy. Check each cookie and third party against your scan. Edit anything that doesn’t match, then click Publish.
The page appears under All Legal Pages, with a shortcode if you want to embed it elsewhere.
How to display your cookie policy
Publishing the page is half the job. Visitors need to find it.
- Footer link. Link the policy from the footer of every page. WPLP Legal Pages can add footer links for you, on every plan.
- Cookie banner link. Put a “Cookie Policy” link in your banner, so visitors can read it before they choose. Most cookie banner plugins, including WPLP Cookie Consent, have a policy link setting. Hide the banner on the cookie policy page itself, so it doesn’t cover the text.
- Privacy policy link. Link to the cookie policy from the cookies section of your privacy policy.
- Cookie settings. Add a link or button in the policy that opens the visitor’s cookie settings, so they can change their choice from the page.
- Popup. WPLP Legal Pages can also show a legal page in a popup.
Setup for the banner: how to add a cookie banner in WordPress. Design rules: cookie consent best practices.
Keep your cookie policy up to date
A cookie policy goes out of date as soon as you add a new tool.
Update it when you:
- Add or remove a plugin, embed, form, or tracking script.
- Start sharing data with a new third party.
- Change how long a cookie lasts or what you use it for.
- See a change in the law for your visitors’ regions.
Change the “Last updated” date each time. If the change adds new non-essential cookies, ask visitors for consent again.
FAQ
What is a cookie policy?
A page that explains which cookies a website uses, what each one does, how long it lasts, who gets the data, and how visitors can accept, refuse, or change their choice.
What is the difference between a privacy policy and a cookie policy?
A privacy policy covers all the personal data you collect: forms, accounts, orders, analytics, and cookies. A cookie policy covers only cookies and similar tracking tools, in more detail. Many sites have both and link them to each other. Some small sites put the cookie information inside the privacy policy instead.
Do I need a cookie banner if I have a cookie policy?
Yes, if you have EU or UK visitors and use non-essential cookies. The policy explains your cookies. The banner gets consent and blocks non-essential cookies until the visitor agrees. Strictly necessary cookies don’t need consent. In California, the CCPA uses opt-out instead, so you need a “Do Not Sell or Share” option, not an opt-in banner.
Does a cookie policy make my site compliant?
No. It covers the disclosure duty. You also need a banner that blocks non-essential cookies before consent (for EU, UK, and India visitors), a privacy policy, and a policy that matches what your site actually sets.
Can I copy another website’s cookie policy?
No. Its cookies, providers, and business details won’t match your site, so the policy would be wrong. The text may also be protected by copyright. Use the checklist and example above, a generator, or a lawyer.
Do I need a lawyer to write a cookie policy?
Not for most small sites. A self-written or generated policy that matches your scan covers the basics. Get legal advice if your site is aimed at children, collects sensitive data, sells data, or has large audiences in several countries.
Do I need a cookie policy for visitors in India?
If your cookies collect personal data from people in India, the DPDP Act asks for a clear notice and consent. The notice and consent duties apply from 14 May 2027. A cookie policy linked from your consent request covers most of the notice.
Is the WPLP cookie policy template free?
No. The GDPR Cookie Policy and Cookies Policy templates are on paid plans, from $8/month or $48/year. The Free plan has 4 templates: Standard Privacy Policy, Terms of Use, DMCA, and Standard CCPA.
This article is general information, not legal advice.