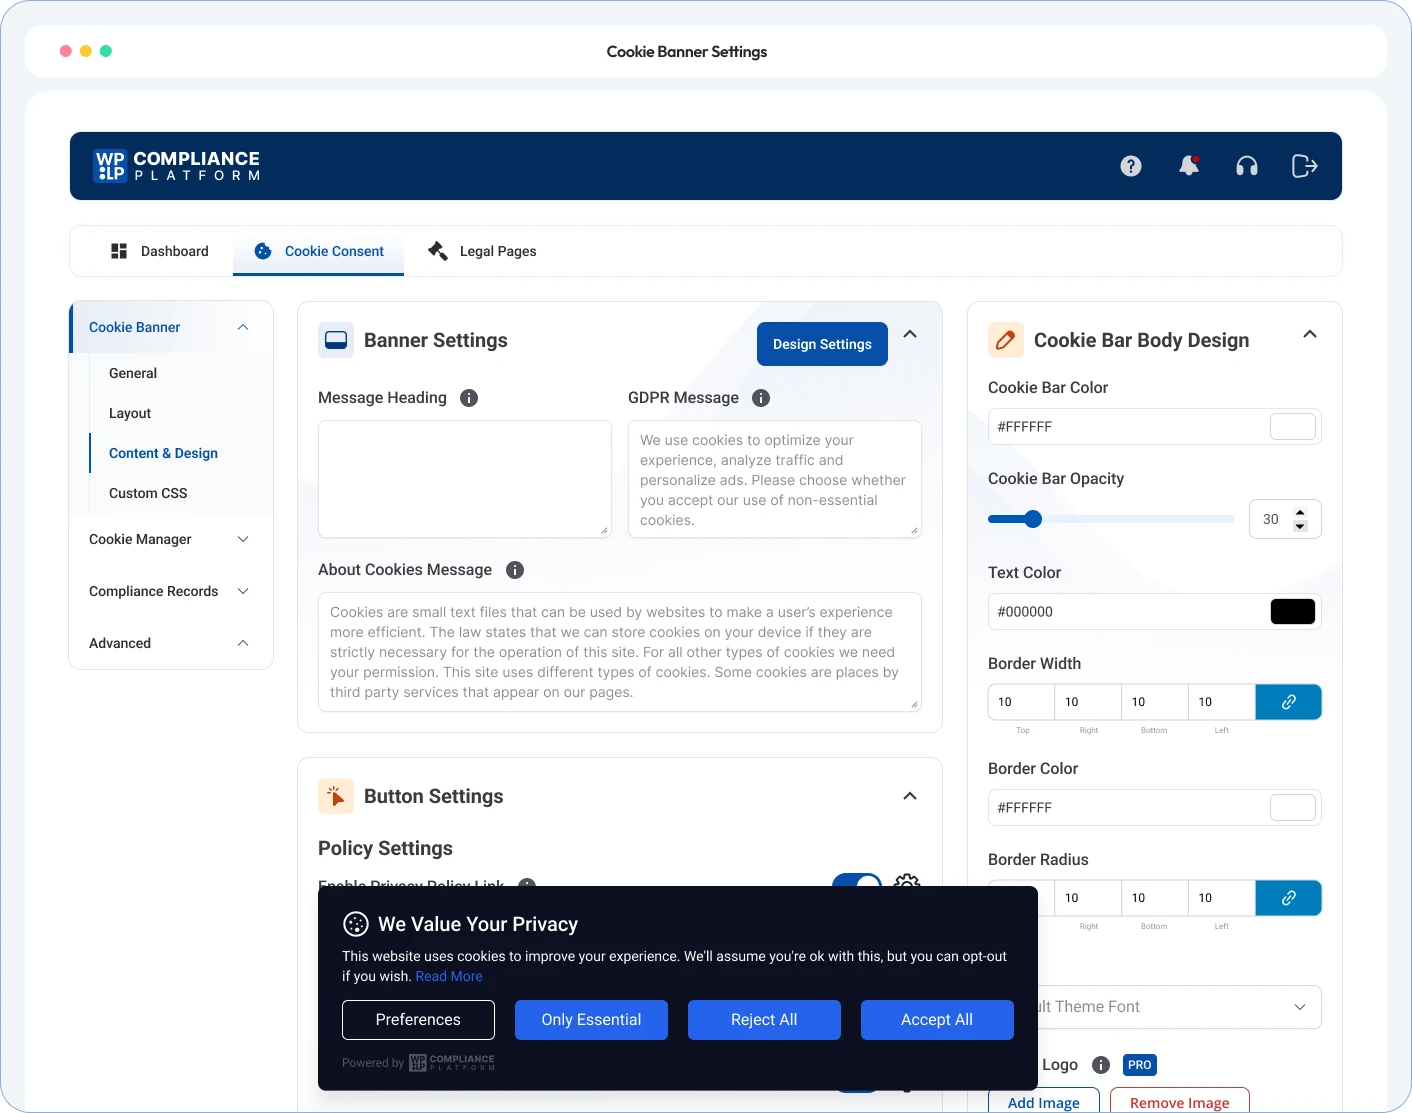
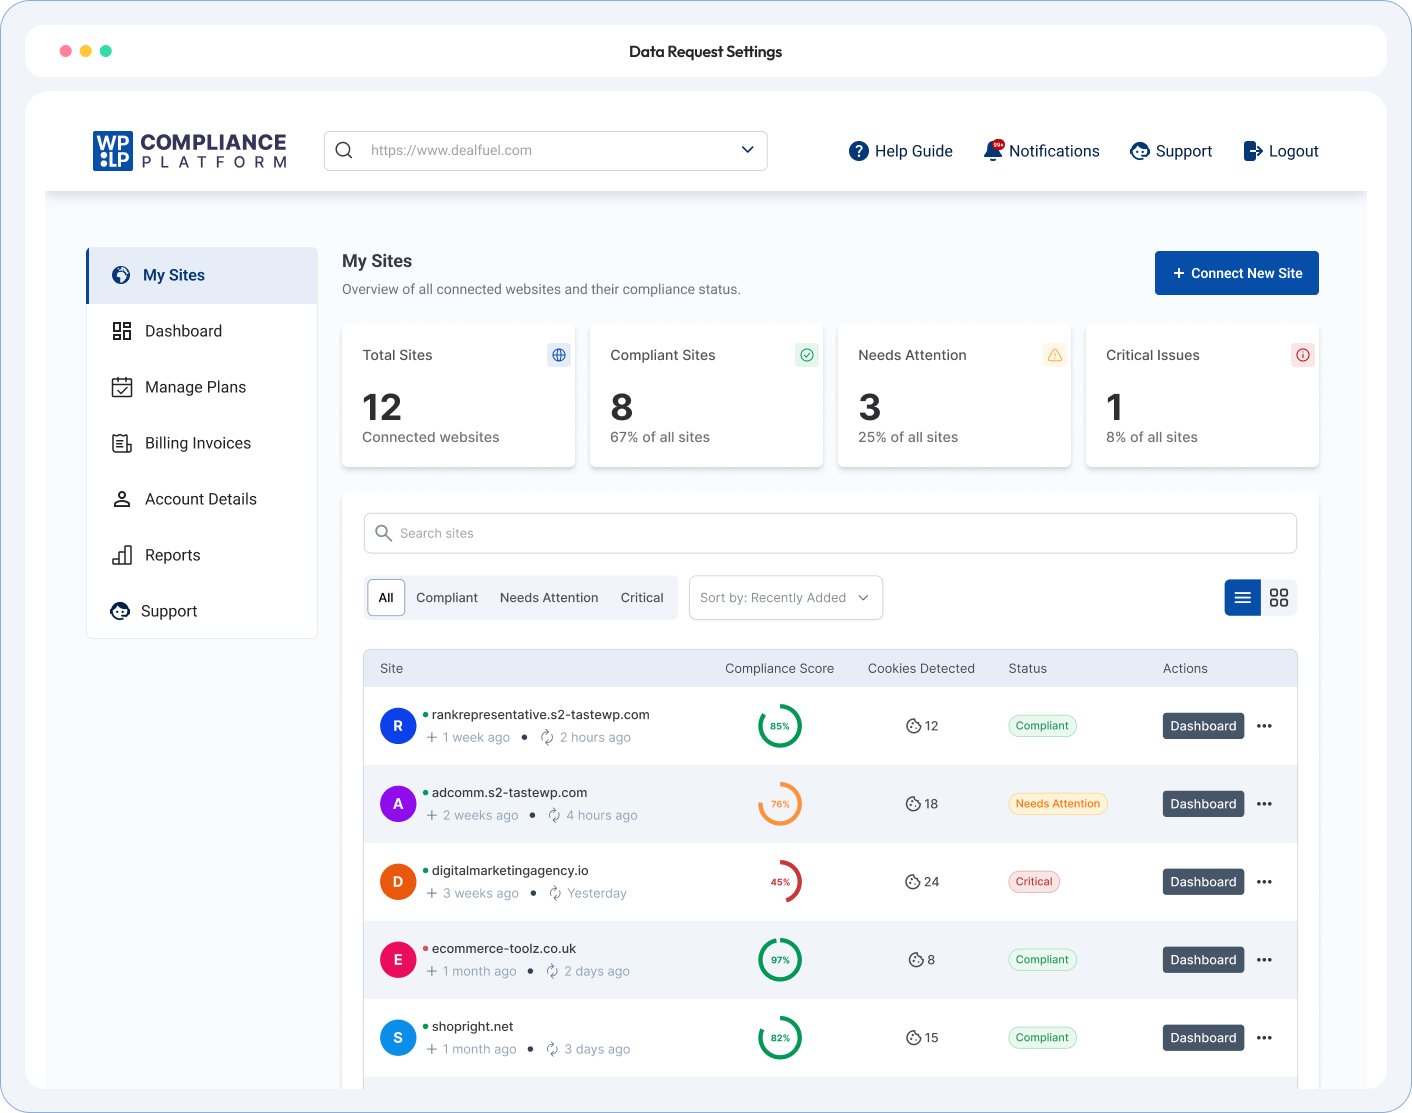
Stop patching disconnected tools. WPLP Compliance combines cookie consent, script-blocking, Google Consent Mode v2 support, and 25+ policy templates into lightweight WordPress plugins. Full EU compliance, without slowing down your site.
Think GDPR doesn’t apply to your business? If even a single visitor from the EU lands on your WordPress site, and your collects their data, GDPR applies to your website.
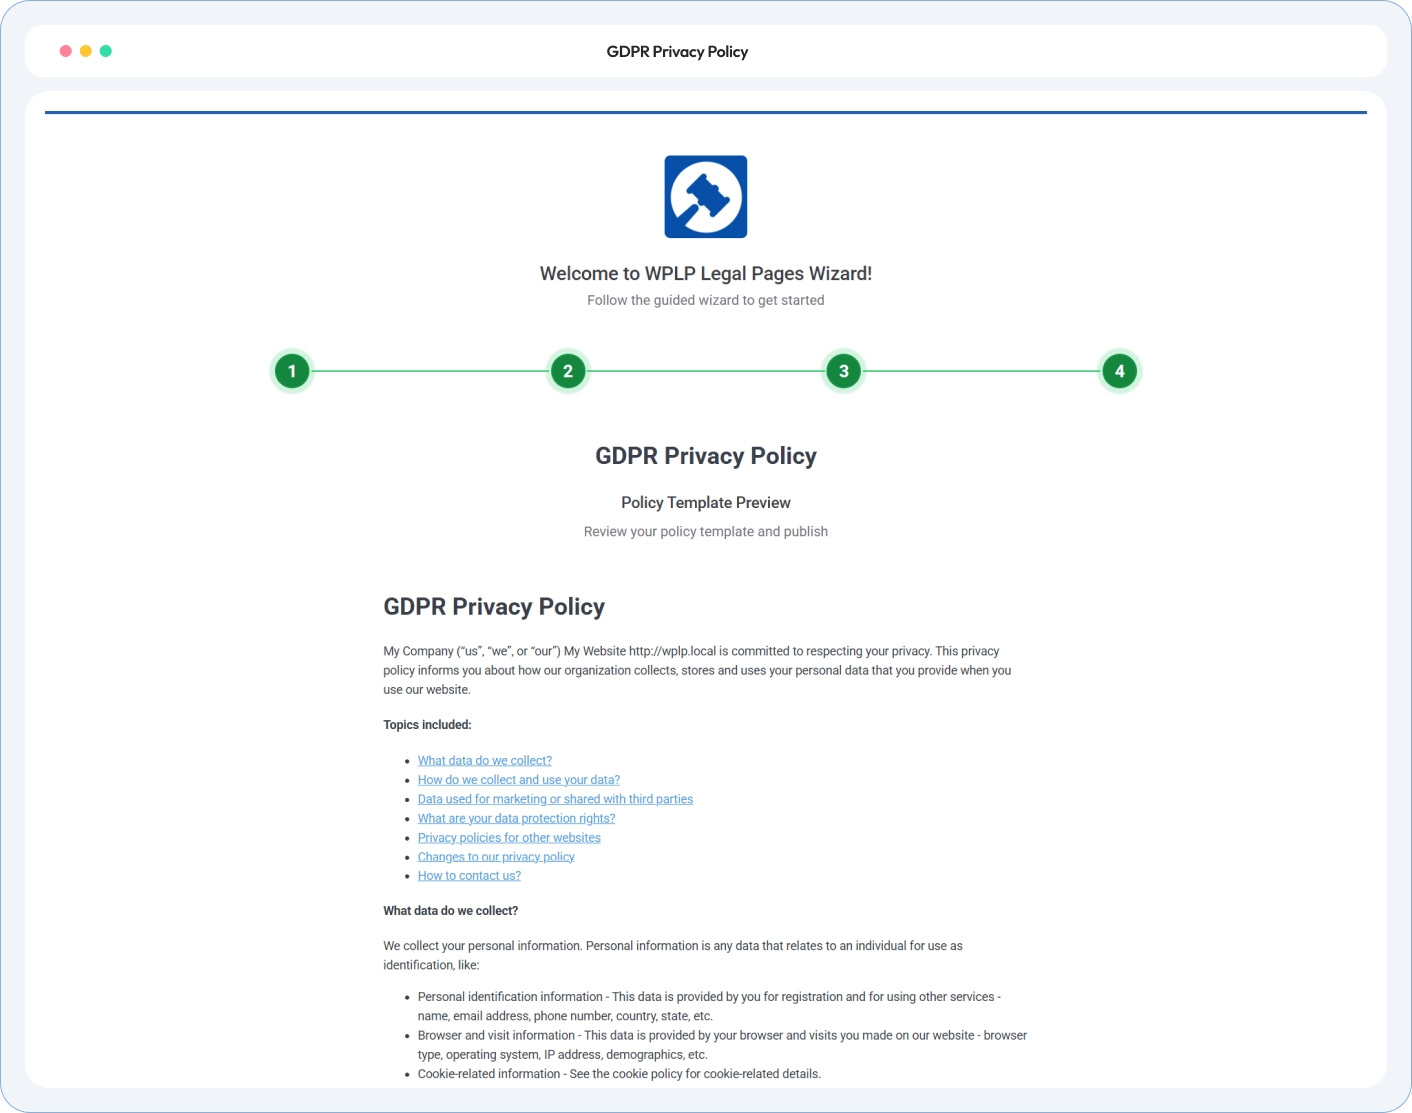
True EU compliance requires both consent controls and accurate legal disclosure. Deploy a fully compliant cookie banner alongside dynamic privacy policies that disclose exactly what your site collects.
Hear from site owners, agencies and developers who simplified their WordPress legal compliance.
• Frequently Asked Questions •
Everything you need to know about cookie consent, legal policy generation, and meeting European privacy requirements on WordPress.
No, core WordPress is not GDPR compliant by default. While it includes tools to export and erase user data, it cannot display cookie banners, block tracking scripts before opt-in consent, or generate dynamic legal policies. Full compliance requires a dedicated plugin like WPLegalPages to suppress analytics, pixels, and cookies until visitors explicitly agree.
Yes, any WordPress website receiving visitors from the European Union or United Kingdom must comply with GDPR, regardless of where the business or server is located. Loading analytics cookies or collecting contact form entries without prior consent violates EU regulations. WPLegalPages provides geo-targeted cookie banners that show consent controls exclusively to EU and UK traffic.
A cookie banner is an active technical mechanism that suppresses tracking scripts until a user opts in. A privacy policy is a legally required document disclosing data processing practices, processors, and user rights. Complete GDPR compliance requires both: active script suppression at the browser level and accurate, synchronized legal documentation published on your WordPress website.
Not when using an optimized compliance architecture. Many plugins degrade Core Web Vitals by running heavy server-side database queries and bulky JavaScript. WPLegalPages avoids speed drops by offloading automated cookie scans to cloud infrastructure and injecting lightweight, vanilla JavaScript banners only on pages where consent controls are necessary.
Under Article 83 of the GDPR, non-compliant websites face statutory fines up to €20 million or 4% of annual global turnover, whichever is higher. Beyond regulatory penalties from authorities like CNIL or the ICO, non-compliance can trigger Google Ads account restrictions and broken GA4 conversion tracking due to strict Google Consent Mode v2 enforcement.
WPLegalPages stores all proof-of-consent logs and user choices directly in your local WordPress database. Unlike third-party SaaS platforms that route visitor data through external servers and charge recurring per-pageview fees, local database storage guarantees 100% data ownership, simplifies data audits, and eliminates recurring tracking costs.
Sign up for our paid plans and get instant access to cookie consent, policy pages, and compliance dashboard.