A cookie policy is a page that lists the cookies your site uses, what each one does, how long it lasts, and how visitors can say no.
If you have visitors in the EU or UK and use analytics, ads, or embeds, you need one. Below: what to put in it, 3 ways to write it, how to publish it on WordPress, and where to link it.
What is a cookie policy?
Cookies are small text files a site stores in the visitor’s browser. Some keep the site working. Others track visitors for analytics and ads.
A cookie policy explains those cookies in plain language. It answers 4 questions for the visitor:
- Which cookies does this site use?
- Why?
- Who else gets the data?
- How do I refuse or change my choice?
The cookie policy and the cookie banner do different jobs. The policy explains. The cookie banner asks for consent and blocks cookies until the visitor agrees. You need both. More on the difference: cookie notice vs cookie policy.
Do you need a cookie policy?
It depends on where your visitors are.
- EU and UK visitors. The ePrivacy Directive (Art. 5(3)) and the UK’s PECR say you must give “clear and comprehensive information” about cookies and get consent before you set non-essential ones. A cookie policy is the standard way to give that information. GDPR applies on top when cookies collect personal data, which most analytics and ad cookies do. See ePrivacy Directive vs GDPR.
- California visitors. The CCPA does not require a separate cookie policy. It requires a privacy policy that discloses the data you collect, including through cookies, and a “Do Not Sell or Share” link if you sell or share data. It applies to businesses over $26,625,000 in annual revenue, or that buy, sell, or share data on 100,000+ California consumers or households, or that earn 50%+ of revenue from selling or sharing data. See our CCPA guide.
- Everyone else. Many privacy laws ask you to disclose tracking, and Google AdSense asks publishers to disclose cookie use. A cookie policy is the simplest way to do it.
If your site sets only strictly necessary cookies (login, cart, security), you don’t need consent for them. You should still list them in your cookie policy or privacy policy.
Essential vs non-essential cookies
This split decides which cookies need consent.
| Essential (strictly necessary) | Non-essential | |
|---|---|---|
| What they do | Keep the site working: login, cart, security, saving the visitor’s cookie choice | Analytics, ads, social media, embeds, some preference cookies |
| Examples | WordPress login cookie, WooCommerce cart cookie | Google Analytics _ga, Meta Pixel _fbp, YouTube embed cookies |
| Consent needed under ePrivacy and GDPR? | No | Yes, before the cookie is set |
| List in the cookie policy? | Yes | Yes |
A cookie counts as strictly necessary only if the site, or a feature the visitor asked for, can’t work without it. “It helps our marketing” does not qualify.
The UK’s 2025 law changes allow a few low-risk cookies, such as some analytics, without consent in limited cases. Asking consent for all non-essential cookies still works in the UK. Get advice before you rely on the exceptions.
More on each type: types of internet cookies, session cookies, analytical cookies, and Google Ads cookies.
What to include in a cookie policy
Use this checklist. It covers what GDPR and the ePrivacy Directive expect.
About the policy
- Your business name and website URL.
- The date the policy was last updated.
- A short, plain explanation of what cookies are, including similar tools such as pixels and local storage.
The cookies
- The categories you use: strictly necessary, preferences, analytics, marketing.
- For each cookie: name, provider (you or a third party), purpose, and duration.
- Whether each cookie is first-party or third-party.
- What data the cookies collect, such as a device ID or IP address.
Sharing and storage
- Third parties that receive data through cookies, for example Google or Meta, with a link to their privacy policies.
- Whether data leaves the EU or UK, and how it is protected.
Consent and control
- Which cookies need consent and which don’t, and why.
- How the visitor accepts, refuses, or changes their choice, with a link or button that opens your cookie settings.
- That visitors can withdraw consent at any time, as easily as they gave it.
- How to block or delete cookies in the browser.
Rights and contact
- The visitor’s rights under GDPR (access, deletion, objection) and how to use them.
- A link to your privacy policy for the full detail on personal data.
- How to contact you with questions.
Before you write anything, run a cookie scan. You can’t list cookies you don’t know about. The WPLP cookie scanner finds and sorts them. Run it again each time you add a plugin, form, embed, or tracking tool, then update the policy.
Cookie policy example
Here is what 3 core sections look like on a small WordPress site that runs WooCommerce, Google Analytics, and the Meta Pixel. Use it to see the level of detail a policy needs. Your cookie names, providers, and durations come from your own scan.
Cookies we use
| Cookie | Provider | Category | Purpose | Duration |
|---|---|---|---|---|
wordpress_logged_in_* | This website | Strictly necessary | Keeps you logged in to your account | Session |
woocommerce_cart_hash | This website | Strictly necessary | Remembers the items in your cart | Session |
_ga | Analytics | Tells visits apart so we can count visitors and see which pages they use | 2 years | |
_fbp | Meta | Marketing | Lets us show you our ads on Facebook and Instagram, and measure them | 90 days |
When we ask for your consent
We set strictly necessary cookies without asking, because the website can’t work without them. We set analytics and marketing cookies only after you agree in our cookie banner. Until then, they stay blocked.
How to change your choice
You can change or withdraw your consent at any time. Click “Cookie settings” at the bottom of any page and switch each category on or off. You can also block or delete cookies in your browser settings. If you block strictly necessary cookies, parts of the website, such as the cart, may stop working.
Short sentences, one cookie per row, and a clear way to say no. That is the standard to aim for in every section on the checklist.
How to create a cookie policy in WordPress with WPLP Legal Pages
WPLP Legal Pages generates legal pages from a questionnaire and publishes them in WordPress.
The cookie policy templates are on paid plans. There are 2: GDPR Cookie Policy for EU and UK visitors, and Cookies Policy for sites outside the EU and UK. The Free plan includes 4 other templates: Standard Privacy Policy, Terms of Use, DMCA, and Standard CCPA.
Step 1: Install the plugin
- In WordPress, go to Plugins > Add New.
- Search for WPLP Legal Pages.
- Click Install Now, then Activate.
Step 2: Add your business details
Open WP Legal Pages in the admin menu. Fill in your business profile: domain, business name, contact details, and address.
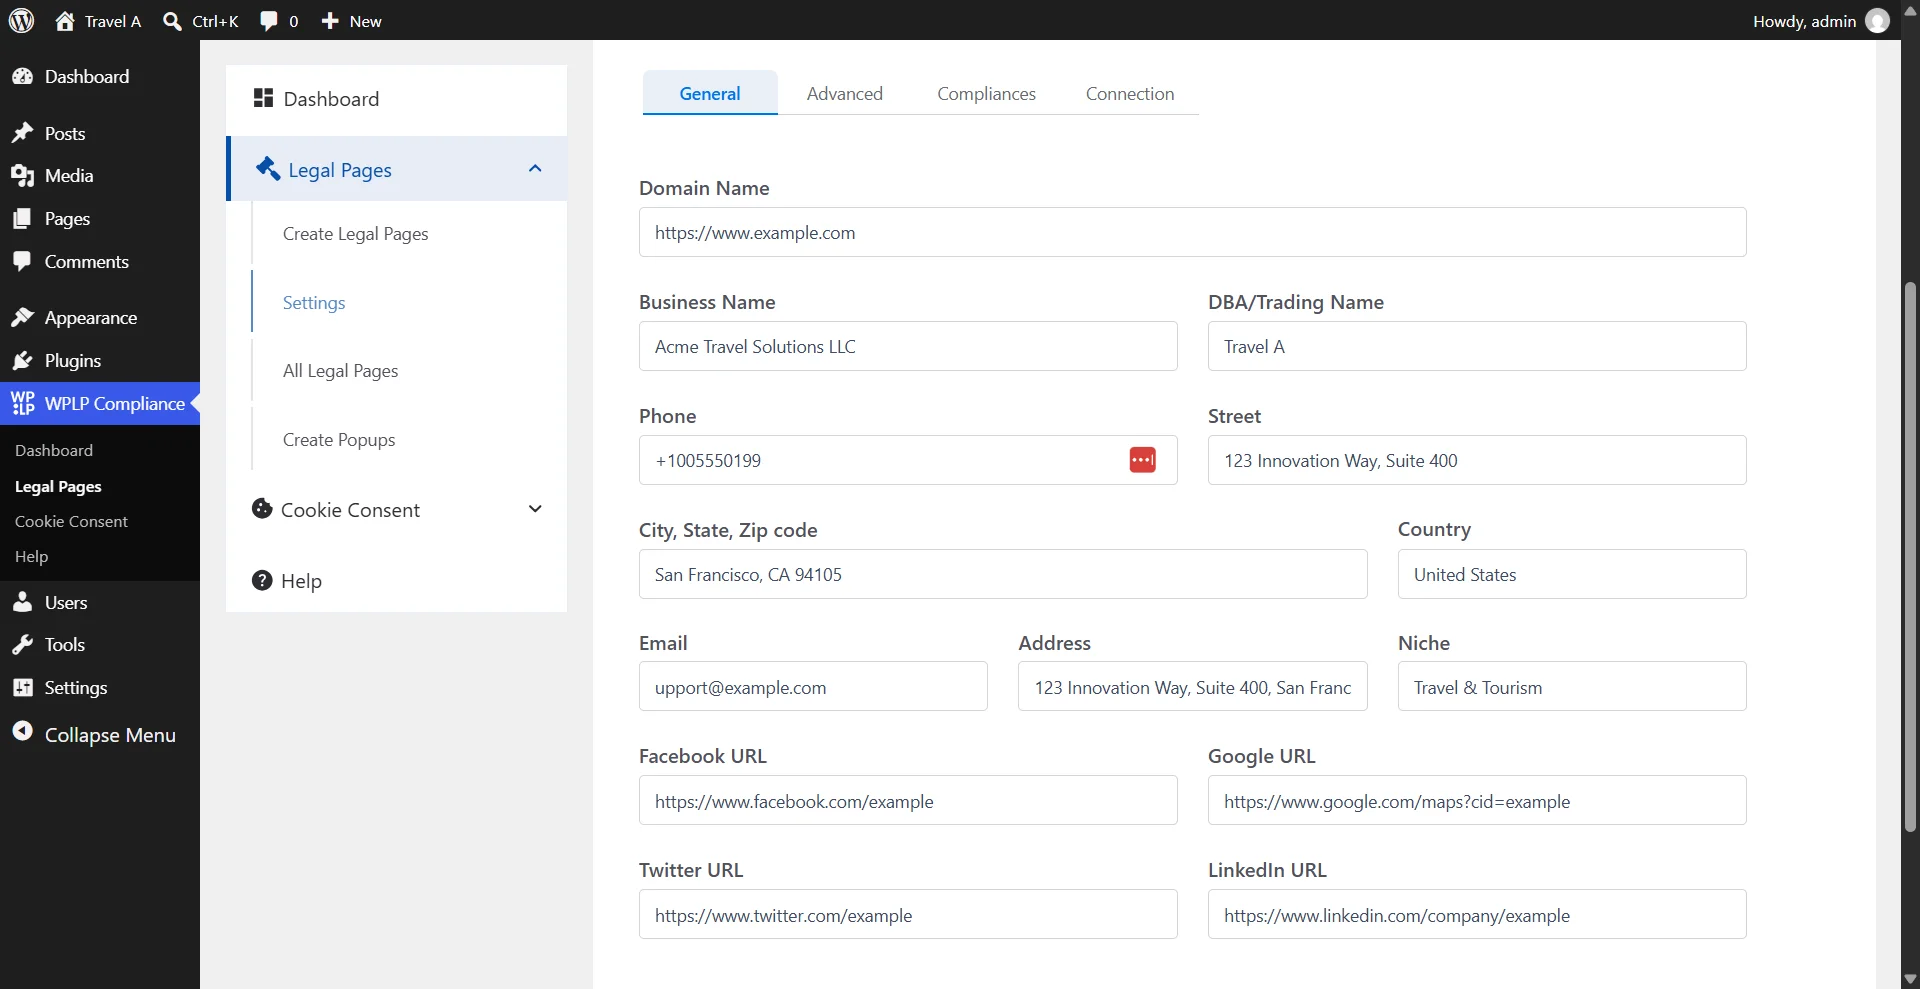
You enter these once. Every legal page you generate uses them.
Step 3: Choose a paid plan
Buy a plan on the pricing page:
| Plan | Price | Sites |
|---|---|---|
| Professional | $8/month or $48/year | Up to 3 |
| Business | $12/month or $72/year | Up to 10 |
| Agency | $28 to $98/month | 25, 50, or 100 |
The pro templates turn on in the plugin you already have. Nothing to reinstall. Every plan includes the full template library of 30+ templates, so the same plan also covers a GDPR privacy policy, terms and conditions, and disclaimers.
Step 4: Pick the cookie policy template
Go to Create Legal Pages and choose:
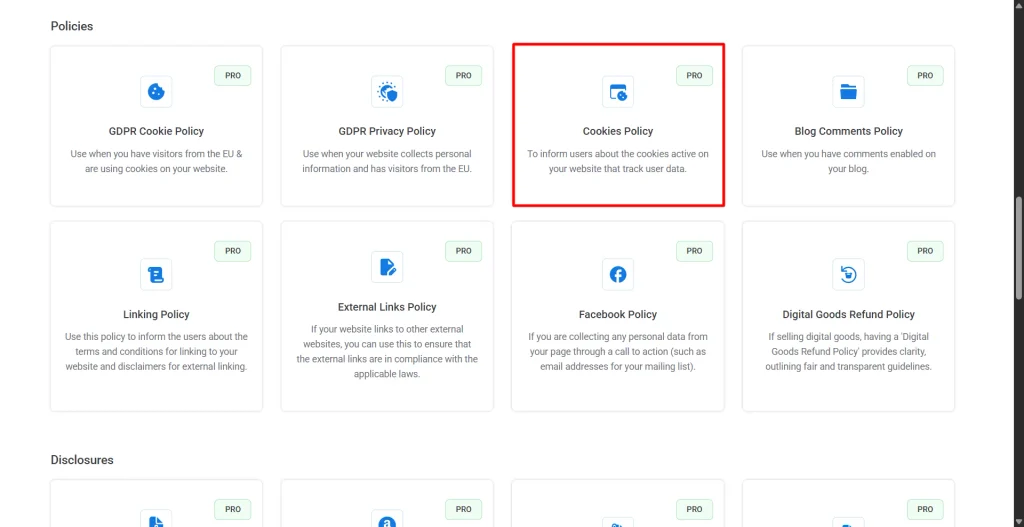
- GDPR Cookie Policy if you have visitors in the EU or UK.
- Cookies Policy if you don’t.
More on the template: GDPR cookie policy generator.
Step 5: Answer the questionnaire
The wizard asks about your site and the cookies you use. Have your cookie scan results open, so your answers match what the site actually sets.
Step 6: Review, edit, and publish
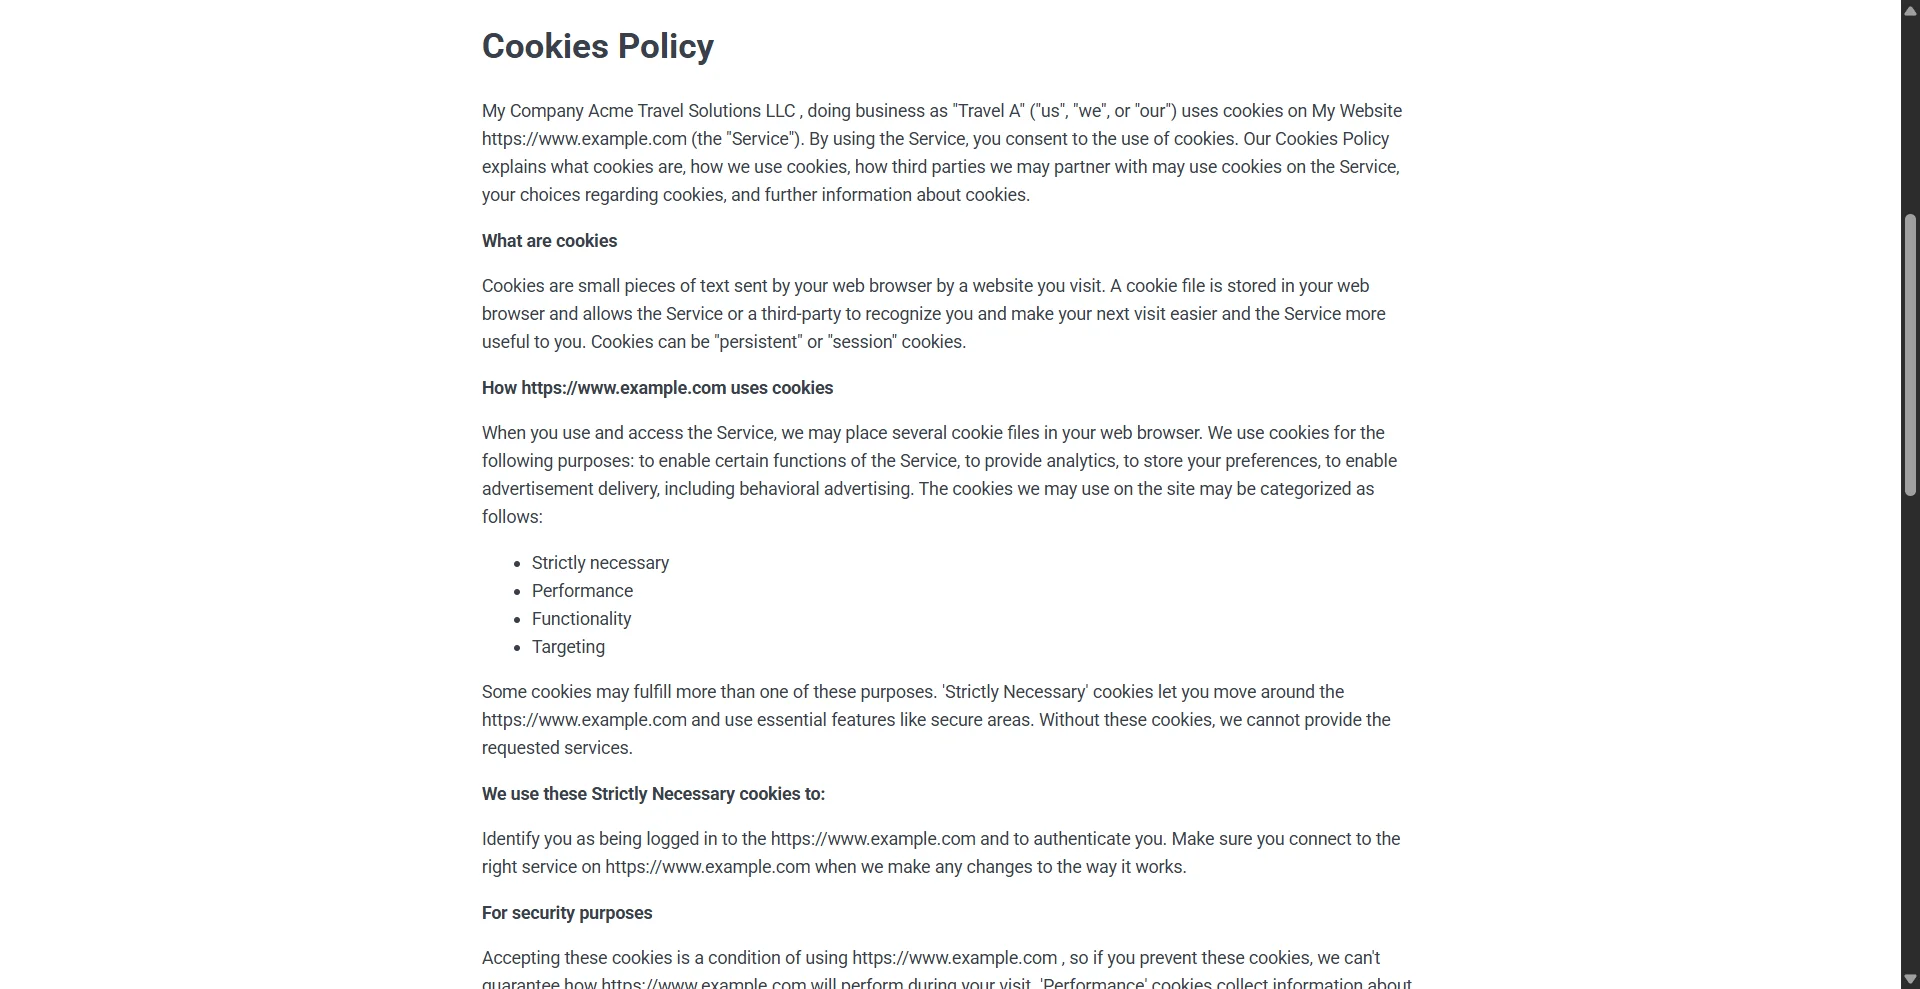
Preview the generated policy. Check each cookie and third party against your scan. Edit anything that doesn’t match, then click Publish.
The page appears under All Legal Pages, with a shortcode if you want to embed it elsewhere.
How to display your cookie policy
Publishing the page is half the job. Visitors need to find it.
- Footer link. Link the policy from the footer of every page. WPLP Legal Pages can add footer links for you, on every plan.
- Cookie banner link. Put a “Cookie Policy” link in your banner, so visitors can read it before they choose. WPLP Cookie Consent has a policy link setting. Hide the banner on the cookie policy page itself, so it doesn’t cover the text.
- Privacy policy link. Link to the cookie policy from the cookies section of your privacy policy.
- Cookie settings. Add a link or button in the policy that opens the visitor’s cookie settings, so they can change their choice from the page.
- Popup. WPLP Legal Pages can also show a legal page in a popup.
Setup for the banner: how to add a cookie banner in WordPress. Design rules: cookie consent best practices.
Keep your cookie policy up to date
A cookie policy goes out of date as soon as you add a new tool.
Update it when you:
- Add or remove a plugin, embed, form, or tracking script.
- Start sharing data with a new third party.
- Change how long a cookie lasts or what you use it for.
- See a change in the law for your visitors’ regions.
Change the “Last updated” date each time. If the change adds new non-essential cookies, ask visitors for consent again.
FAQ
A page that explains which cookies a website uses, what each one does, how long it lasts, who gets the data, and how visitors can accept, refuse, or change their choice.
A privacy policy covers all the personal data you collect: forms, accounts, orders, analytics, and cookies. A cookie policy covers only cookies and similar tracking tools, in more detail. Many sites have both and link them to each other. Some small sites put the cookie information inside the privacy policy instead.
Yes, if you have EU or UK visitors and use non-essential cookies. The policy explains your cookies. The banner gets consent and blocks non-essential cookies until the visitor agrees. Strictly necessary cookies don’t need consent. In California, the CCPA uses opt-out instead, so you need a “Do Not Sell or Share” option, not an opt-in banner.
No. The GDPR Cookie Policy and Cookies Policy templates are on paid plans, from $8/month or $48/year. The Free plan has 4 templates: Standard Privacy Policy, Terms of Use, DMCA, and Standard CCPA.