Data privacy laws (also called data protection regulations) set rules for how organizations collect, use, store, and share personal data. This guide covers 48 laws across 6 regions, including all 20 US state laws in force. For each one, you get who it covers, when it took effect, and the maximum fine.
What the 48 laws are. The 29 numbered sections below (California’s CCPA included), plus the 19 other US state laws in force, listed in section 7. We include each country’s main privacy law that applies to websites and online businesses, Germany’s and Ireland’s national GDPR laws as examples of EU national rules, and every US state law in force in 2026. Laws passed but not yet in force are listed separately.
Before you rely on a date or a fine, check the law’s official text or the regulator’s guidance. The main sources are linked at the end of this article. This guide is general information, not legal advice.
What is data privacy law?
Data privacy laws, also known as data protection laws, protect individuals’ personal information. They govern how data is collected, stored, processed, and shared, so people keep control over how their information is used.
Key elements of data privacy laws often include:
- Consent: Organizations must get valid consent before collecting or processing personal information when the law requires it. Consent should be informed, specific, and freely given. See implied vs explicit cookie consent.
- Purpose limitation: Collect personal data only for legitimate purposes, and use it only for the reasons you gave at the time of collection.
- Data minimization: Collect only the data you need for a specific purpose.
- Data security: Use technical and organizational measures to protect personal information from unauthorized access, loss, or misuse.
- Data subject rights: Most privacy laws give people the right to access, correct, delete, or transfer their personal data. See our guide to data subject access requests.
- Accountability: Organizations are expected to document their data practices and show how they comply.
Why do we need data privacy laws?
Websites, apps, and ad networks collect more personal data every year. Without rules, that data can be misused, leading to privacy breaches, identity theft, and fraud.
Large data breaches affecting millions of users have pushed governments to set clear standards and hold organizations accountable for the data they collect.
Data privacy laws by country: comparison table
The “Approach” column shows the general rule. Each law has exceptions, so check the law itself before you rely on it.
The “Maximum penalty” column mixes different kinds of penalty: administrative fines on companies (for example GDPR, LGPD, PIPL), civil penalties per violation (US states), criminal fines (for example Japan, the Philippines), fines on individuals (Switzerland), and fines for specific offences (Canada, New Zealand). They aren’t directly comparable, so check which kind applies before you compare risk.
| Law | Country / region | In force since | Who it applies to | Approach | Maximum penalty |
|---|---|---|---|---|---|
| GDPR | European Union | May 2018 | Organizations that process EU residents’ data, wherever they are based | Legal basis needed (consent is one of 6) | €20 million or 4% of global annual turnover |
| UK GDPR + DPA 2018 | United Kingdom | January 2021 (UK GDPR); 2018 (DPA) | Organizations that process UK residents’ data | Legal basis needed | £17.5 million or 4% of global annual turnover |
| Revised FADP | Switzerland | September 2023 | Private companies and federal bodies processing data in Switzerland | Notice-based; consent in specific cases | CHF 250,000 (criminal fines on responsible individuals) |
| CCPA / CPRA | California, US | January 2020 (CPRA changes: 2023) | For-profit businesses that meet revenue or data thresholds | Opt-out of sale and sharing | $7,988 per intentional violation (2025 inflation-adjusted figure) |
| 19 other US state laws | US states | 2023 to 2026 | Businesses that meet each state’s thresholds | Opt-out; opt-in for sensitive data in most states | Varies by state, often $7,500 per violation |
| PIPEDA | Canada | 2001 (fully in force 2004) | Private-sector organizations in commercial activity | Consent-based (express or implied) | CAD 100,000 per offence (certain offences) |
| Law 25 | Quebec, Canada | Phased: 2022 to 2024 | Organizations that handle Quebec residents’ data | Consent-based | CAD 25 million or 4% of worldwide turnover |
| Privacy Act 1988 (amended 2024) | Australia | 1988 (amended December 2024) | Most businesses with annual turnover above AUD 3 million, plus some smaller ones | Notice-based; consent for sensitive data | AUD 50 million, 3x the benefit, or 30% of turnover |
| PDPA | Thailand | June 2022 | Organizations that process data of people in Thailand | Legal basis needed | THB 5 million (administrative fine) |
| APPI | Japan | 2005 (amended 2022) | Businesses that handle personal information in Japan | Consent for third-party sharing and sensitive data | JPY 100 million (corporate criminal fine) |
| Privacy Act 2020 | New Zealand | December 2020 | Agencies and businesses in New Zealand | Notice-based | NZD 10,000 |
| Data Privacy Act | Philippines | 2012 (rules 2016) | Organizations that process data in the Philippines | Legal basis needed (consent is one option) | Criminal fines up to PHP 5 million and imprisonment |
| PIPA | South Korea | September 2011 (amended 2023) | Organizations that process data in South Korea | Consent-based, with exceptions | 3% of total annual revenue |
| PDPA | Singapore | 2014 (amended 2020) | Private organizations in Singapore | Consent-based, with deemed consent | 10% of Singapore turnover or SGD 1 million |
| PDPA | Malaysia | November 2013 (amended 2024) | Commercial data processing in Malaysia | Consent-based, with exceptions | MYR 1 million |
| PDPO | Hong Kong | 1996 (amended 2021) | Anyone who controls personal data in Hong Kong | Notice-based; consent for new purposes and direct marketing | Fines and imprisonment for specific offences |
| DPDP Act | India | Phased from November 2025 to May 2027 | Organizations that process digital personal data in India or offer goods and services to people in India | Consent-based, with “legitimate uses” | INR 250 crore per breach (penalties apply from 13 May 2027) |
| PIPL | China | November 2021 | Organizations that handle data of people in China, including from abroad | Consent-based; separate consent for sensitive data and transfers | RMB 50 million or 5% of prior-year revenue |
| KVKK | Turkey | April 2016 (amended 2024) | Data controllers processing data in Turkey | Legal basis needed | Administrative fines, updated yearly |
| PDPL | Oman | February 2023 | Organizations that process data in Oman | Consent-based, with exceptions | From OMR 500 to OMR 500,000 depending on the severity of the violation |
| PDPL | Saudi Arabia | September 2023 (enforced September 2024) | Organizations that process data of people in Saudi Arabia | Legal basis needed | SAR 5 million (doubled for repeat violations) |
| LGPD | Brazil | September 2020 (sanctions from August 2021) | Organizations that process data in Brazil or of people in Brazil | Legal basis needed (10 bases) | 2% of Brazil revenue, capped at BRL 50 million per violation |
| Federal Data Protection Law | Mexico | March 2025 | Private parties that process personal data | Consent; express consent for sensitive data | Up to 320,000 UMA (about USD 1.8 million) |
| Law 21.719 | Chile | December 2026 | Organizations that process data of people in Chile | Legal basis needed | 20,000 UTM, or up to 4% of annual revenue for repeat violations by large companies |
| Law 1581 of 2012 | Colombia | 2012 | Organizations that process data in Colombia | Prior authorization (consent) | 2,000 monthly minimum wages |
| Law 25,326 | Argentina | 2000 | Organizations that process data in Argentina | Consent-based, with exceptions | From ARS 1,000 to ARS 100,000 |
| LOPDP | Ecuador | May 2021 (sanctions from May 2023) | Organizations that process data in Ecuador | Legal basis needed | Fines around USD $259,644.01 |
| POPIA | South Africa | July 2020 (enforced July 2021) | Organizations that process data in South Africa | Legal basis needed | ZAR 10 million and/or up to 10 years’ imprisonment |
Germany’s BDSG and Ireland’s Data Protection Act 2018 add national rules to the GDPR. GDPR fines apply to them.
1. General Data Protection Regulation (GDPR), EU
The General Data Protection Regulation (GDPR) governs how organizations process personal data of people in the EU. It’s the most influential privacy law worldwide, and many countries modeled their own laws on it.
- In force: 25 May 2018
- Applies to: Any organization that offers goods or services to people in the EU or monitors their online behavior, wherever it is based.
- Key requirement:A legal basis for every processing activity. Cookie consent comes from a separate law, the ePrivacy Directive, as each EU country applies it: non-essential cookies generally need prior consent, and strictly necessary cookies are exempt. See ePrivacy Directive vs GDPR.
- Max fine: €20 million or 4% of global annual turnover, whichever is higher. See the biggest GDPR fines so far.
2. Germany: Federal Data Protection Act (BDSG)
The BDSG adds German rules to the GDPR.
- In force: May 2018 (current version)
- Applies to: Organizations that process personal data in Germany.
- Key requirement: Most companies with 20 or more people who regularly process personal data must appoint a data protection officer.
- Max fine: GDPR fines apply.
3. Ireland: Data Protection Act 2018
The Irish DPA puts the GDPR into Irish law and sets up the Data Protection Commission (DPC). Many large tech companies have their EU headquarters in Ireland, so the DPC leads many cross-border GDPR cases.
- In force: May 2018
- Applies to: Organizations that process personal data in Ireland.
- Max fine: GDPR fines apply.
4. United Kingdom: UK GDPR, DPA 2018, and the Data (Use and Access) Act 2025
After Brexit, the UK kept its own version of the GDPR. The UK GDPR and the Data Protection Act 2018 work together. See DPA vs GDPR for the differences.
The Data (Use and Access) Act 2025 became law on 19 June 2025. Since 5 February 2026, it removes consent for some low-risk cookies, such as analytics cookies used only to improve a service, as long as visitors are told and can object. It also raises the maximum fine for cookie and e-marketing breaches from £500,000 to £17.5 million or 4% of global turnover.
- Applies to: Organizations that process UK residents’ data.
- Key requirement: A legal basis for processing, plus consent for most non-essential cookies.
- Max fine: £17.5 million or 4% of global annual turnover.
5. Switzerland: Revised Federal Act on Data Protection (FADP)
The revised Swiss Federal Act on Data Protection (FADP) replaced Switzerland’s 1992 law.
- In force: 1 September 2023
- Applies to: Private companies and federal bodies that process personal data in Switzerland, and foreign companies whose processing affects people in Switzerland.
- Key requirement: Tell people when you collect their data, and keep a record of processing activities.
- Max fine: CHF 250,000. Fines are charged to the responsible individuals, not the company.
6. California Consumer Privacy Act (CCPA), amended by the CPRA
The California Consumer Privacy Act (CCPA) was the first comprehensive US state privacy law. The California Privacy Rights Act (CPRA) expanded it from 2023 and created the California Privacy Protection Agency to enforce it. See CPRA vs CCPA for what changed.
- In force: 1 January 2020. The CPRA changes took effect on 1 January 2023.
- Applies to: For-profit businesses that meet one of the law’s thresholds (for example, annual revenue above a set amount, or buying, selling, or sharing data of 100,000 or more California consumers or households).
- Key requirement: A “Do Not Sell or Share My Personal Information” link, and support for Global Privacy Control signals.
- Max fine: $2,663 per violation and $7,988 per intentional violation (2025 inflation-adjusted figures). See the biggest CCPA fines and penalties.
7. Other US state privacy laws
20 US states have comprehensive privacy laws in force in 2026. Most follow the Virginia model: people can opt out of the sale of their data, targeted ads, and profiling, and most states require opt-in consent for sensitive data.
| State | Law | In force from | Status |
|---|---|---|---|
| California | CCPA / CPRA | 1 January 2020 | In force |
| Virginia | Consumer Data Protection Act | 1 January 2023 | In force |
| Colorado | Colorado Privacy Act | 1 July 2023 | In force |
| Connecticut | Data Privacy Act | 1 July 2023 | In force |
| Utah | Consumer Privacy Act | 31 December 2023 | In force |
| Florida | Digital Bill of Rights (narrow: applies only to very large companies) | 1 July 2024 | In force |
| Oregon | Consumer Privacy Act | 1 July 2024 | In force |
| Texas | Data Privacy and Security Act | 1 July 2024 | In force |
| Montana | Consumer Data Privacy Act | 1 October 2024 | In force |
| Delaware | Personal Data Privacy Act | 1 January 2025 | In force |
| Iowa | Consumer Data Protection Act | 1 January 2025 | In force |
| Nebraska | Data Privacy Act | 1 January 2025 | In force |
| New Hampshire | Privacy Act | 1 January 2025 | In force |
| New Jersey | Data Privacy Act | 15 January 2025 | In force |
| Tennessee | Information Protection Act | 1 July 2025 | In force |
| Minnesota | Consumer Data Privacy Act | 31 July 2025 | In force |
| Maryland | Online Data Privacy Act | 1 October 2025 | In force |
| Indiana | Consumer Data Protection Act | 1 January 2026 | In force |
| Kentucky | Consumer Data Protection Act | 1 January 2026 | In force |
| Rhode Island | Data Transparency and Privacy Protection Act | 1 January 2026 | In force |
| Louisiana | Louisiana Data Privacy Act (SB 386) | 1 January 2027 | Passed 2026, not yet in force |
| Oklahoma | SB 546 | 1 January 2027 | Passed 2026, not yet in force |
| Alabama | Alabama Personal Data Protection Act (HB 351) | 1 May 2027 | Passed 2026, not yet in force |
| Vermont | Vermont Data Privacy and Online Surveillance Act (S.71) | 1 January 2028 | Passed 2026, not yet in force |
Penalties vary by state. Virginia and Texas allow up to $7,500 per violation. Each state’s attorney general enforces its law. California also has its own privacy agency.
For a full breakdown, see our complete guide to US state privacy laws.
8. Canada: PIPEDA
The Personal Information Protection and Electronic Documents Act (PIPEDA) is Canada’s federal private-sector privacy law.
- In force: 2001, fully in force since 2004.
- Applies to: Private-sector organizations that collect, use, or disclose personal information in commercial activity. Alberta, British Columbia, and Quebec have their own laws that apply in place of PIPEDA for activity inside those provinces.
- Key requirement: Meaningful consent, and only collecting data for purposes a reasonable person would find appropriate.
- Max fine: CAD 100,000 per offence for certain offences.
Reform status: Bill C-27, which would have replaced PIPEDA with the Consumer Privacy Protection Act, died when Parliament was prorogued in January 2025. The government introduced Bill C-36, the Protecting Privacy and Consumer Data Act, on 15 June 2026. It is not law yet, so PIPEDA still applies.
9. Quebec: Law 25
Law 25 updated Quebec’s private-sector privacy law. It’s the strictest privacy law in Canada.
- In force: Phased, from September 2022 to September 2024.
- Applies to: Organizations that handle personal information of people in Quebec.
- Key requirement: A named person in charge of personal information, privacy impact assessments, and consent for tracking technologies.
- Max fine: CAD 25 million or 4% of worldwide turnover (penal offences).
- More: What is Quebec’s Law 25?
10. Australia: Privacy Act 1988 and the 2024 amendments
Australia’s Privacy Act and its 13 Australian Privacy Principles (APPs) govern how organizations handle personal information. The Privacy and Other Legislation Amendment Act 2024 added higher penalties, a new tort for serious invasions of privacy, and a plan for a Children’s Online Privacy Code.
- Applies to: Most businesses with annual turnover above AUD 3 million, plus some smaller businesses, such as health service providers.
- Key requirement: A clear, up-to-date privacy policy, and consent before collecting sensitive information.
- Max fine: AUD 50 million, 3 times the benefit gained, or 30% of adjusted turnover, whichever is greatest.
11. Thailand: Personal Data Protection Act (PDPA)
- In force: 1 June 2022, after two delays.
- Applies to: Organizations that collect, use, or disclose personal data of people in Thailand, including some based abroad.
- Key requirement: A legal basis for processing, and explicit consent for sensitive data.
- Max fine: THB 5 million (administrative). Criminal penalties also apply.
12. Japan: Act on the Protection of Personal Information (APPI)
- In force: Passed in 2003, fully in force in 2005. Major amendments took effect on 1 April 2022.
- Applies to: Businesses that handle personal information of people in Japan.
- Key requirement: Consent before sharing personal data with third parties, and breach reports to the regulator.
- Max fine: JPY 100 million for companies (criminal fine).
13. New Zealand: Privacy Act 2020
- In force: 1 December 2020
- Applies to: Agencies and businesses in New Zealand, and overseas businesses that operate there.
- Key requirement: Report serious privacy breaches to the Privacy Commissioner and the affected people.
- Max fine: NZD 10,000 for certain offences.
14. Philippines: Data Privacy Act of 2012
- In force: 2012, with implementing rules from 2016.
- Applies to: Organizations that process personal data in the Philippines.
- Key requirement: A data protection officer, and security measures to protect personal data.
- Max fine: Up to PHP 5 million, plus imprisonment for some offences. The National Privacy Commission enforces it.
15. South Korea: Personal Information Protection Act (PIPA)
- In force: September 2011. Major amendments in 2023.
- Applies to: Organizations that process personal data in South Korea.
- Key requirement: Specific, informed consent in many cases, with separate consent for sensitive data.
- Max fine: 3% of total annual revenue.
16. Singapore: Personal Data Protection Act (PDPA)
- In force: Passed in 2012, data protection rules in force since 2014. Amended in 2020.
- Applies to: Private-sector organizations that collect, use, or disclose personal data in Singapore.
- Key requirement: Consent (including deemed consent), and breach notification.
- Max fine: 10% of annual Singapore turnover for organizations with more than SGD 10 million turnover, otherwise SGD 1 million.
17. Malaysia: Personal Data Protection Act (PDPA)
- In force: Passed in 2010, in force since November 2013. Amended in 2024.
- Applies to: Personal data processed in commercial transactions in Malaysia.
- Key requirement: The 2024 amendments added mandatory breach notification, data protection officers, and a right to data portability.
- Max fine: MYR 1 million.
18. Hong Kong: Personal Data (Privacy) Ordinance (PDPO)
- In force: 1996. Amended in 2012 (direct marketing) and 2021 (doxxing).
- Applies to: Anyone who controls the collection, holding, processing, or use of personal data in Hong Kong.
- Key requirement: 6 data protection principles, and consent before using personal data for direct marketing.
- Max fine: Fines and imprisonment for specific offences. The Privacy Commissioner for Personal Data enforces it.
19. India: Digital Personal Data Protection Act (DPDP Act)
The Digital Personal Data Protection Act is India’s first comprehensive privacy law.
- Passed: August 2023. The DPDP Rules were notified on 13 November 2025 and phase in over 18 months:
- 13 November 2025: the Data Protection Board was set up, with the Board’s rules.
- 13 November 2026: rules for registered consent managers.
- 13 May 2027: most other duties, including notice, consent, data subject rights, and penalties.
- Applies to: Organizations that process digital personal data in India, and organizations abroad that offer goods or services to people in India.
- Key requirement: Clear notice and consent, with extra protections for children’s data.
- Max fine: INR 250 crore per breach, from 13 May 2027. The Data Protection Board of India enforces it.
20. China: Personal Information Protection Law (PIPL)
- In force: 1 November 2021
- Applies to: Organizations that handle personal information of people in China, including organizations outside China.
- Key requirement: Separate consent for sensitive data and for cross-border transfers, plus a security assessment or standard contract for many transfers.
- Max fine: RMB 50 million or 5% of the previous year’s revenue.
21. Turkey: Law on the Protection of Personal Data (KVKK)
- In force: April 2016. Amended in 2024 (cross-border transfer rules).
- Applies to: Data controllers that process personal data in Turkey.
- Key requirement: Registration with the data controllers’ registry (VERBIS) for many organizations.
- Max fine: Administrative fines, updated each year.
22. Oman: Personal Data Protection Law
- In force: 13 February 2023 (Royal Decree 6/2022).
- Applies to: Organizations that process personal data in Oman.
- Key requirement: Consent before processing, with some exceptions, and a permit for processing sensitive data.
- Max fine: From OMR 500 to OMR 500,000 depending on the severity of the violation
23. Saudi Arabia: Personal Data Protection Law (PDPL)
- In force: Passed in September 2021, in force on 14 September 2023. Enforced since 14 September 2024.
- Applies to: Organizations that process personal data of people in Saudi Arabia, including from abroad.
- Key requirement: A legal basis for processing, and controls on transfers outside the Kingdom.
- Max fine: SAR 5 million, doubled for repeat violations. Disclosing sensitive data with intent to harm can bring up to 2 years in prison.
24. Brazil: Lei Geral de Proteção de Dados (LGPD)
Brazil’s Lei Geral de Proteção de Dados (LGPD) is modeled on the GDPR.
- In force: 18 September 2020. Sanctions apply from August 2021.
- Applies to: Organizations that process personal data in Brazil or of people in Brazil.
- Key requirement: One of 10 legal bases for processing, and a data protection officer (encarregado).
- Max fine: 2% of revenue in Brazil, capped at BRL 50 million per violation.
25. Mexico: Federal Law on the Protection of Personal Data Held by Private Parties
Mexico replaced its 2010 law with a new law on 21 March 2025. The same reform abolished the old regulator (INAI) and moved its powers to a federal ministry.
- Applies to: Private individuals and companies that process personal data.
- Key requirement: A privacy notice, and express consent for sensitive data.
- Max fine: Up to 320,000 UMA (about USD 1.8 million). Fines can double when sensitive data is involved.
26. Chile: Law 21.719
Chile passed a new data protection law in December 2024, based on the GDPR. It creates a new regulator, the Personal Data Protection Agency.
- In force: 1 December 2026
- Applies to: Organizations that process personal data of people in Chile.
- Key requirement: A legal basis for processing, and new rights such as data portability.
- Max fine: 20,000 UTM. Large companies with repeat violations can be fined up to 4% of annual revenue.
27. Colombia: Law 1581 of 2012
- In force: 2012
- Applies to: Organizations that process personal data in Colombia.
- Key requirement: Prior, express authorization from the person, and registration of databases with the regulator for many organizations.
- Max fine: 2,000 monthly legal minimum wages. The Superintendence of Industry and Commerce (SIC) enforces it.
28. Argentina: Personal Data Protection Law (Law 25,326)
- In force: 2000
- Applies to: Organizations that process personal data in Argentina.
- Key requirement: Consent before processing, with exceptions, and registration of databases.
- Max fine: From ARS 1,000 to ARS 100,000.
29. Ecuador: Organic Law on Personal Data Protection (LOPDP)
- In force: May 2021. Sanctions apply from May 2023.
- Applies to: Organizations that process personal data in Ecuador.
- Key requirement: A legal basis for processing, and breach notification.
- Max fine: Fines around USD $259,644.01.
30. South Africa: Protection of Personal Information Act (POPIA)
- In force: Passed in 2013, most sections in force on 1 July 2020. Enforced since 1 July 2021.
- Applies to: Organizations that process personal information in South Africa.
- Key requirement: An information officer registered with the Information Regulator.
- Max fine: ZAR 10 million and/or up to 10 years’ imprisonment.
How to comply with global data privacy laws
These 5 steps cover the core of most laws on this page:
- Map your data. List what personal data your site collects (forms, analytics, cookies, payments), why, and who you share it with. See types of internet cookies.
- Publish a privacy policy. Say what you collect, why, how long you keep it, and how people can use their rights. See how to create a privacy policy for your website.
- Block non-essential cookies until consent, where the law requires it. In the EU (ePrivacy Directive) and the UK, analytics and ad cookies generally wait for opt-in consent, with a few national exceptions. US state laws mostly use opt-out instead.
- Log consent. Keep a record of who agreed to what, and when. See how long to keep consent logs.
- Handle access requests. Set up a way for people to ask for, correct, or delete their data, and answer within the legal deadline.
How WPLP helps on WordPress
1. Publish a privacy policy: WPLP Legal Pages builds your privacy policy from your answers to a few questions about your site. It publishes the policy as a page on your own domain. The free plan includes 4 templates: Privacy Policy, Terms of Use, DMCA, and a CCPA notice. Paid plans add 30+ more.

2. Block cookies until consent: WPLP Cookie Consent scans your site for cookies and scripts. It holds the tracking ones back until a visitor clicks Accept, so analytics and ad tags don’t load first. Both features are on the free plan.
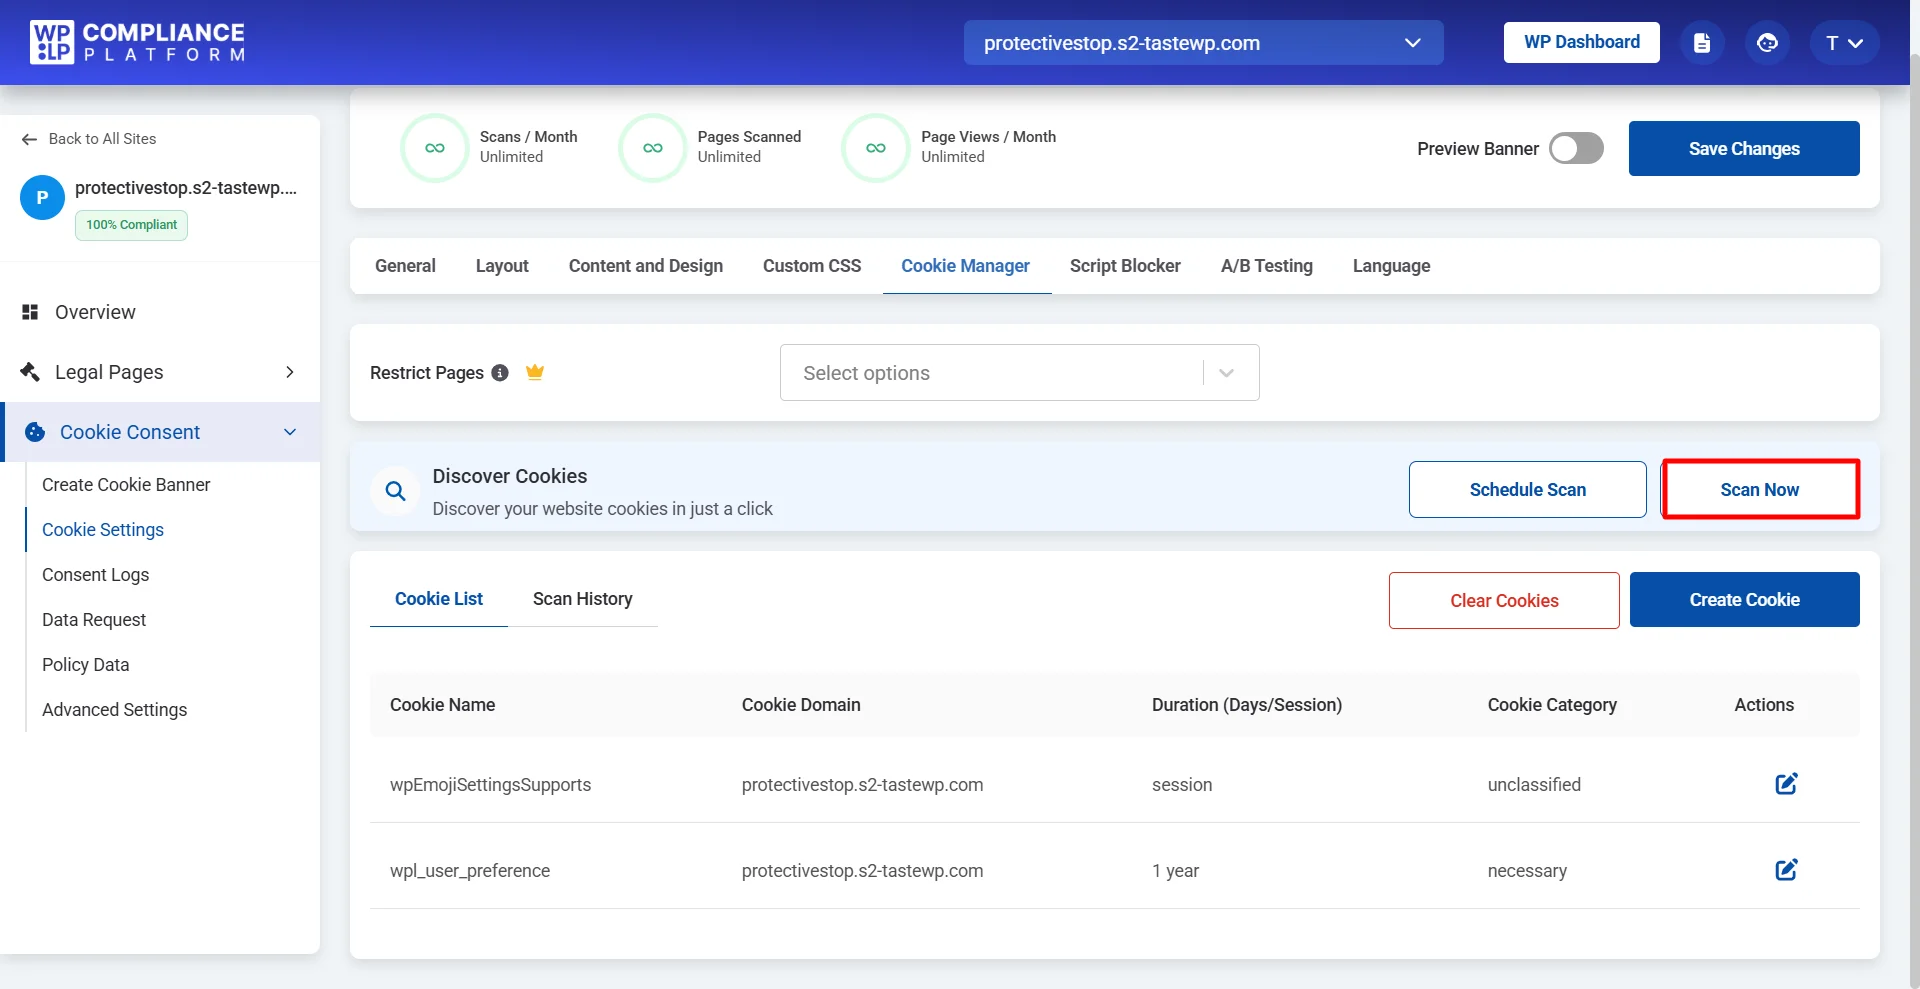
3. Log consent: Each choice a visitor makes is saved in your own WordPress database, and you can export the log as a CSV.
Many laws, one banner. On paid plans, WPLP Cookie Consent checks where each visitor is and shows the banner for the law that applies there. A visitor from the EU sees a GDPR banner, and a visitor from California sees a CCPA banner.
FAQs
Usually the laws of where your visitors are, not only where your business is. A US-based store that sells to customers in France must follow the GDPR. An Indian SaaS company with users in California may fall under the CCPA if it meets the thresholds.
They require businesses to protect personal data, get consent where needed, and give people control over their information. Breaking them can bring fines, lawsuits, and damage to your reputation.
Most laws give people the right to access their data, correct or delete it, and know how it’s used. Many also add rights to data portability, to restrict processing, and to opt out of certain uses, such as the sale of their data.
Yes. The GDPR applies to organizations outside the EU if they offer goods or services to people in the EU or monitor their behavior online.
Government regulators or data protection authorities. Examples: the Information Commissioner’s Office (UK), the California Privacy Protection Agency (US), and the Data Protection Board of India.
Conclusion
Privacy laws now cover most of the world’s internet users, and new ones keep arriving. Chile’s law starts in December 2026, India’s rules phase in through 2027, and 4 more US states passed laws in 2026.
Start with the laws that match where your visitors are. Then work through the 5-step checklist above, and review this list once a year. For a wider list of what your site needs, see website legal requirements.
If you liked reading this article, you might also like:
- Best Privacy Policy Generators for Your Website
- Most Common Privacy Policy Issues to Avoid
- Difference Between Disclaimer and Privacy Policy & How to Create Them
Need a privacy policy and cookie banner that match the laws your visitors fall under? Try the WPLP Compliance Platform.